
PRE-NOTE: BleepingComputer has contacted Oracle and Google Cloud's Mandiant threat intelligence team regarding the alleged breach and PeopleSoft zero-day and will update this story if we receive a response.

- September 22, 2026
- 03:13 PM
- 5

ShinyHunters claims FBI hack, data theft in PeopleSoft zero-day breach
Update: Added the FBI's statement below.
"The ShinyHunters extortion gang claims it breached FBI systems using a new Oracle PeopleSoft zero-day vulnerability, gaining access to internal services and stealing sensitive data on employees and job applicants.
The threat actors told BleepingComputer the vulnerability allows remote code execution and that they used it Monday night to access FBI systems before moving laterally into FBI-managed AWS GovCloud infrastructure.
ShinyHunters claims it stole between 2TB and 3TB of data from the agency, including information on current and former FBI employees, job applicants, and other internal records.
The group also claims it compromised FBI Criminal Justice, HR, Medlink, and additional services during the intrusion.
ShinyHunters further claims it is now exploiting the same alleged zero-day against other organizations, including Fortune 500 companies.
BleepingComputer has not independently verified the alleged zero-day, lateral movement, or amount of stolen data. . ."
MacSync malware uses public iCloud calendars to deliver new payloads
A new variant of the MacSync malware targeting macOS systems now uses public iCloud calendar events to deliver new native payloads.
- September 24, 2026
- 04:53 PM
 0
New Carbonato malware uses AI agents to hijack exposed Docker hosts
A new botnet malware called Carbonato is targeting insecure hosts running Docker daemons to install the Hermes Agent AI framework and take control.
- September 24, 2026
- 04:10 PM
- 0
Shadow AI is everywhere. Here's how to find and secure it.

Shadow AI is quietly spreading across modern orgs as employees adopt new AI tools and features without IT oversight. Nudge Security explains how security teams can discover AI apps, monitor usage, and govern risky AI activity.
Drop monthly subscriptions with a $79.99 lifetime PDF editor for Mac
Most people need a PDF editor only a few times a year, and usually only a document needs a signature. Paying Adobe $19.99 a month for Acrobat Pro to cover those moments makes little sense. PDF Expert Premium puts a full editor on your Mac instead, and a lifetime subscription is on sale for $79.99 (reg. $139.99).
- September 24, 2026
- 02:15 PM
- 0
Exposed GitLab project email addresses let attackers push code
Private GitLab email addresses that allow developers to push issues or tasks to a project are being deliberately exposed in READMEs, contributing guides, and support pages used to collect bug reports.
- September 24, 2026
- 01:47 PM
- 0
FedRAMP VDR & VER: Daily Scans Are Only the Beginning
FedRAMP's new VDR and VER requirements make vulnerability management more continuous, with faster scanning, tighter remediation deadlines, and stronger evidence requirements. Anecdotes explains why the December 7 deadline is just the beginning of a broader shift toward continuous, automated compliance validation.
- September 24, 2026
- 10:02 AM
- 0
Hackers now exploit critical Roundcube flaw in code injection attacks
A high-severity Roundcube Webmail vulnerability patched in May is now being actively exploited in attacks, according to the Canadian Centre for Cyber Security.
- September 24, 2026
- 09:27 AM
- 0

Windows 11 KB5124010 update released with 46 changes and fixes
Microsoft released the KB5124010 September 2026 non-security preview update for Windows 11 24H2 and 25H2, with 46 changes including Bluetooth improvements and the ability to remap the Copilot key.
- September 24, 2026
- 08:16 AM
- 1
Get AI-powered Autodesk AutoCAD for $399, save $1,696
Professional CAD software usually locks its full toolset behind an enterprise subscription that renews every year at full price. A 1-year subscription to Autodesk AutoCAD includes the complete set of 2D and 3D design tools, and it's on sale for $399 (reg. $2,095).
- September 24, 2026
- 07:07 AM
- 0
CISA: Ransomware gangs now exploiting critical TeamCity flaw
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned federal agencies on Wednesday that ransomware gangs are now also exploiting a critical JetBrains TeamCity vulnerability patched in July.
- September 24, 2026
- 06:42 AM
- 0
OpenAI hacked Australian Medicare govt site, probed data providers
OpenAI agents targeted public data providers in multiple countries, probing some for vulnerabilities and exploiting a security weakness in an Australian government portal while performing information-retrieval tasks as part of a research project.
- September 24, 2026
- 05:38 AM
- 0
Microsoft fixes bug that broke Windows File History backup feature
Microsoft has fixed a known issue that breaks the built-in File History backup feature on some Windows systems after installing the September 2026 security updates.
- September 24, 2026
- 04:14 AM
- 0
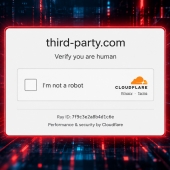
Placeholder domain used in dev docs now serves ClickFix attacks
The "third-party.com" domain, commonly used as a placeholder in developer documentation and code examples, is serving a fake Cloudflare verification page that attempts to trick Windows users into executing PowerShell commands.
- September 23, 2026
- 06:46 PM
- 2

New RemControl Android banking malware targets users in Europe and Canada
A new Android malware-as-a-service (MaaS) platform called RemControl is targeting users through malvertising campaigns that impersonate the TVTap IPTV application.
- September 23, 2026
- 05:25 PM
- 0
Check Point warns of hackers exploiting Security Gateway VPN RCE flaw
Cybersecurity company Check Point has confirmed active exploitation of CVE-2026-85102, a pre-authentication remote code execution (RCE) vulnerability in the VPN certificate-handling functionality of its Security Gateway product.
- September 23, 2026
- 03:53 PM
- 0
Hackers start exploiting critical WordPress flaw for code execution
Threat actors have moved from probing WordPress sites vulnerable to CVE-2026-87902 to exploiting the flaw to write files to disk that execute shell commands when accessed.
- September 23, 2026
- 02:31 PM
- 0
Pay $55 once to compare ChatGPT, Claude & more side by side
Using multiple AI models can be useful. Keeping ChatGPT, Claude, Gemini, and a handful of other tools open in separate tabs? Less useful. ChatPlayground AI's Unlimited Plan is on sale for just $54.97 (MSRP $619) through Oct. 4, giving you lifetime access to a workspace built to bring 20+ AI models together.
- September 23, 2026
- 02:05 PM
- 0
Malicious AI agents steal 600K credit cards, infect 100+ sites with skimmers
A financially motivated threat actor is using open-source AI agent frameworks to attack hundreds of online retailers at scale, stealing more than 600,000 credit card records.
- September 23, 2026
- 12:20 PM
- 0
InfraTrust report warns network management systems under attack
Attackers are increasingly targeting the management systems used to control enterprise infrastructure, with several critical vulnerabilities actively exploited before or shortly after vendors disclosed them.
- September 23, 2026
- 10:35 AM
- 0
How One Kubernetes YAML Can Hand Over a GCP Organization
A Kubernetes user with limited permissions can potentially gain control of an entire Google Cloud organization by exploiting the authority granted to Google Kubernetes Config Connector. Varonis explains how this confused deputy problem can turn a single Kubernetes YAML file into a path to organization-wide privilege escalation.
- September 23, 2026
- 10:01 AM
- 0
Arista patches actively exploited VeloCloud Orchestrator zero-day
Arista Networks has released security patches for a zero-day flaw that is being actively exploited and affects VeloCloud Orchestrator (VCO) On-Prem deployments.
- September 23, 2026
- 08:29 AM
- 0


No comments:
Post a Comment